Linux Server Hardening & CIS Security Audit
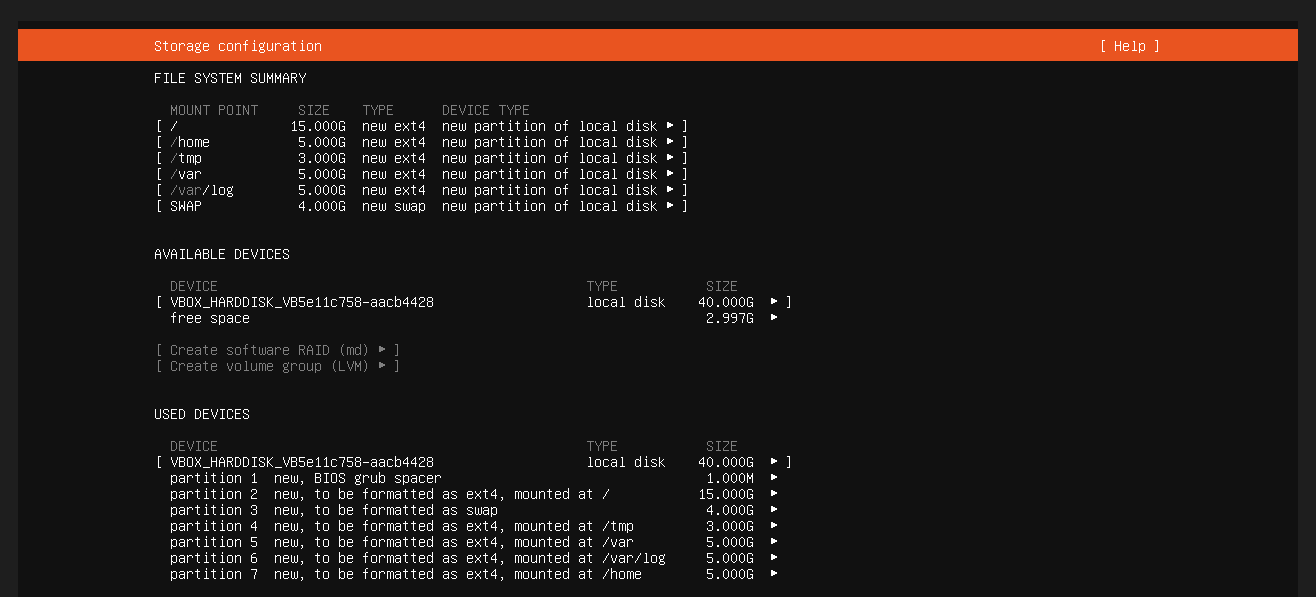
Engineered an enterprise-style Linux defense-in-depth hardening home lab on Ubuntu Server 24.04 LTS in VirtualBox. Began with secure Filesystem Hierarchy Standard (FHS) custom disk partitioning across 6 dedicated partitions (/ 15G, swap 4G, /tmp 3G, /var 5G, /var/log 5G, and /home 5G) to enforce isolated mount policies against payload staging. Analyzed raw authentication logs (auth.log, last, lastb) across simulated failed SSH attempts to isolate PAM edge cases, including grep false negatives on invalid user queries and sudo noise. Implemented and validated restrictive mount flags (nodev, nosuid, noexec) on /tmp with execution denial proofs, recorded comprehensive pre-hardening baselines across 96 CIS checklist controls, and architected a planned 21-function modular Bash auditing script to evaluate compliance with clear PASS/FAIL reporting.
Constructed a 6-partition isolated filesystem architecture, enforced nodev/nosuid/noexec execution boundaries on /tmp, mapped 96 CIS Benchmark controls across 6 categories, and designed a 21-function automated compliance verification engine.
Key Metrics & Measurable Impact
Empirical audit telemetry across FHS filesystem partitioning, CIS Benchmark controls, and authentication forensics.
Dedicated mounts for /, swap, /tmp, /var, /var/log, and /home to restrict binary execution
Comprehensive checklist across 6 categories: Filesystem, Services, Network, Logging, Auth, and Maintenance
Automated checks evaluating system compliance, permissions, and service states
Structured evidence across Phase 1 (29), Phase 2 (30), and Phase 3 (2)
Authentication failure forensics mapped between lastb records and raw auth.log events
21 completed milestones, 3 in progress, 127 planned across manual hardening and scripting
Work Artifacts & Key Evidence
Selected technical screenshots and logs. Use the side arrows to scroll or click any card to inspect.
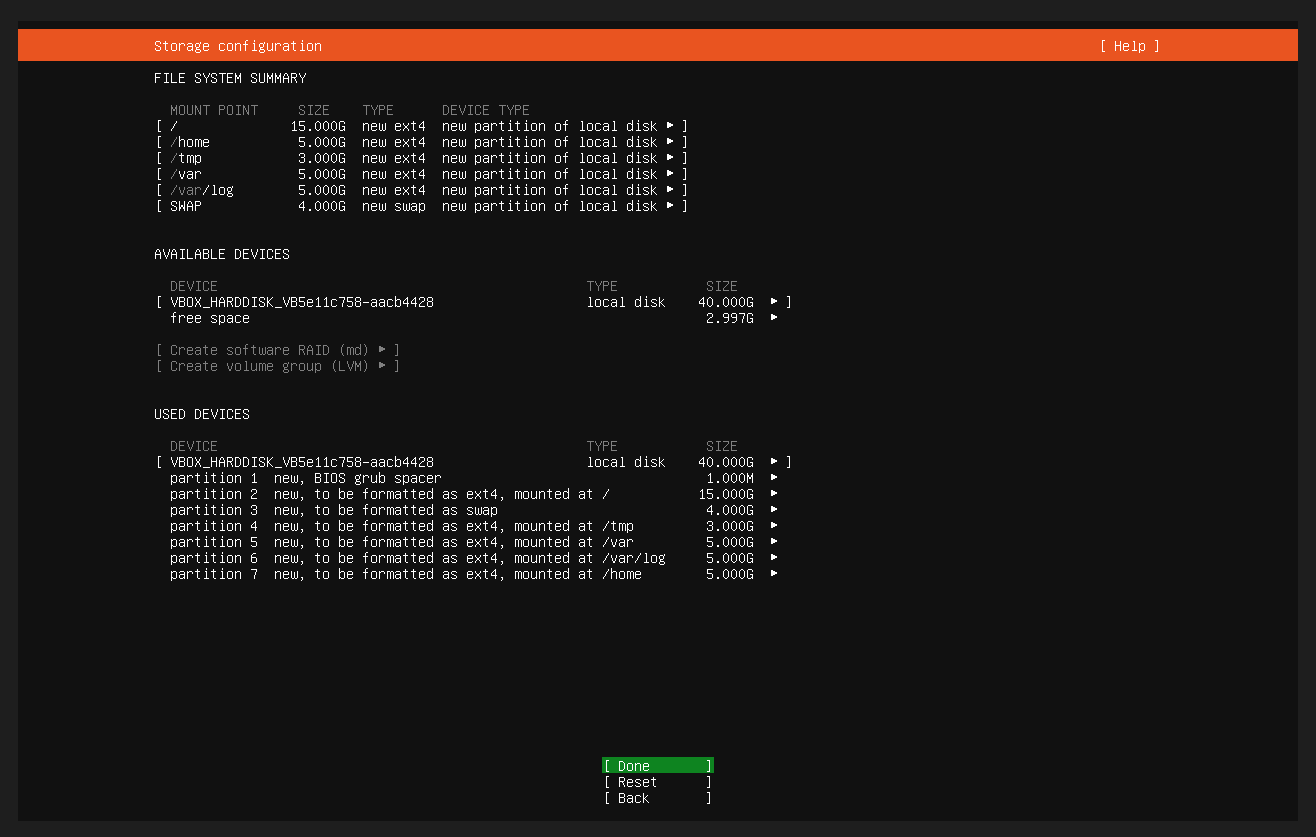
Custom 6-Partition Storage Architecture
Pre-installation custom storage architecture: 6 isolated partitions establishing dedicated security boundaries across mount points.
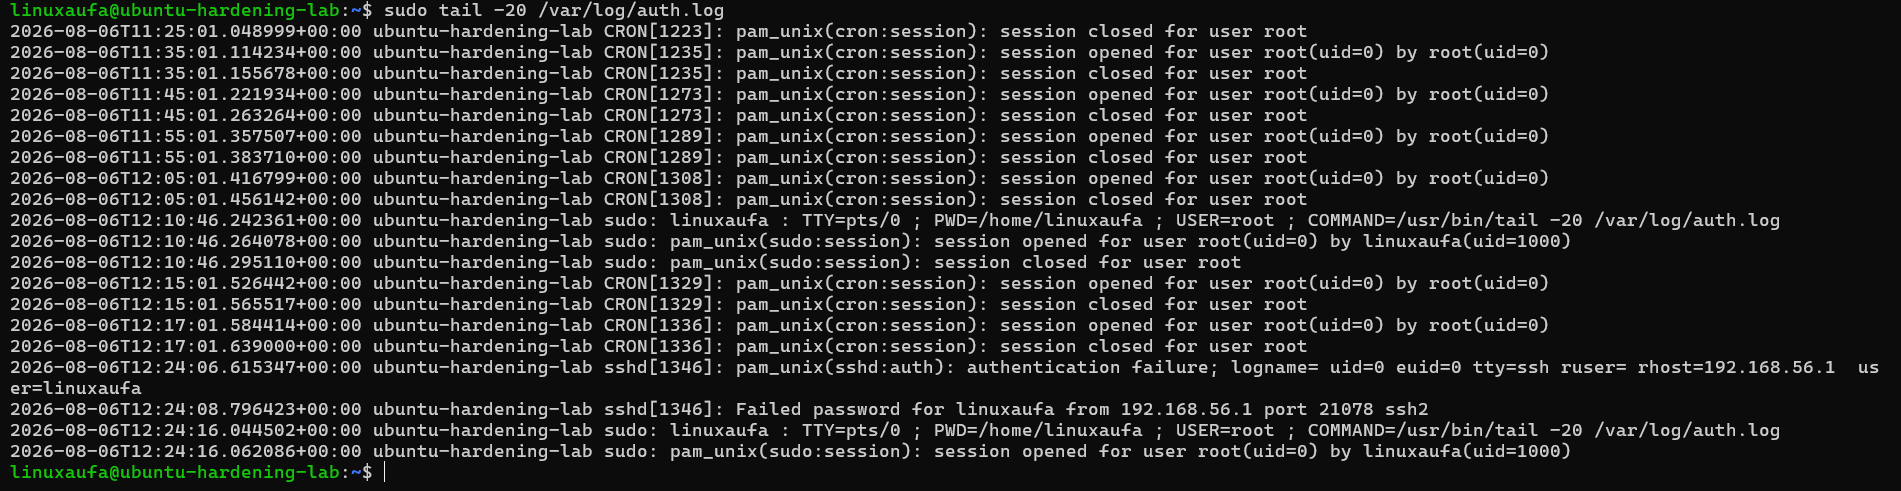
Authentication Telemetry in auth.log
Failed SSH authentication telemetry captured in auth.log with full source IP attribution and timestamp correlation.
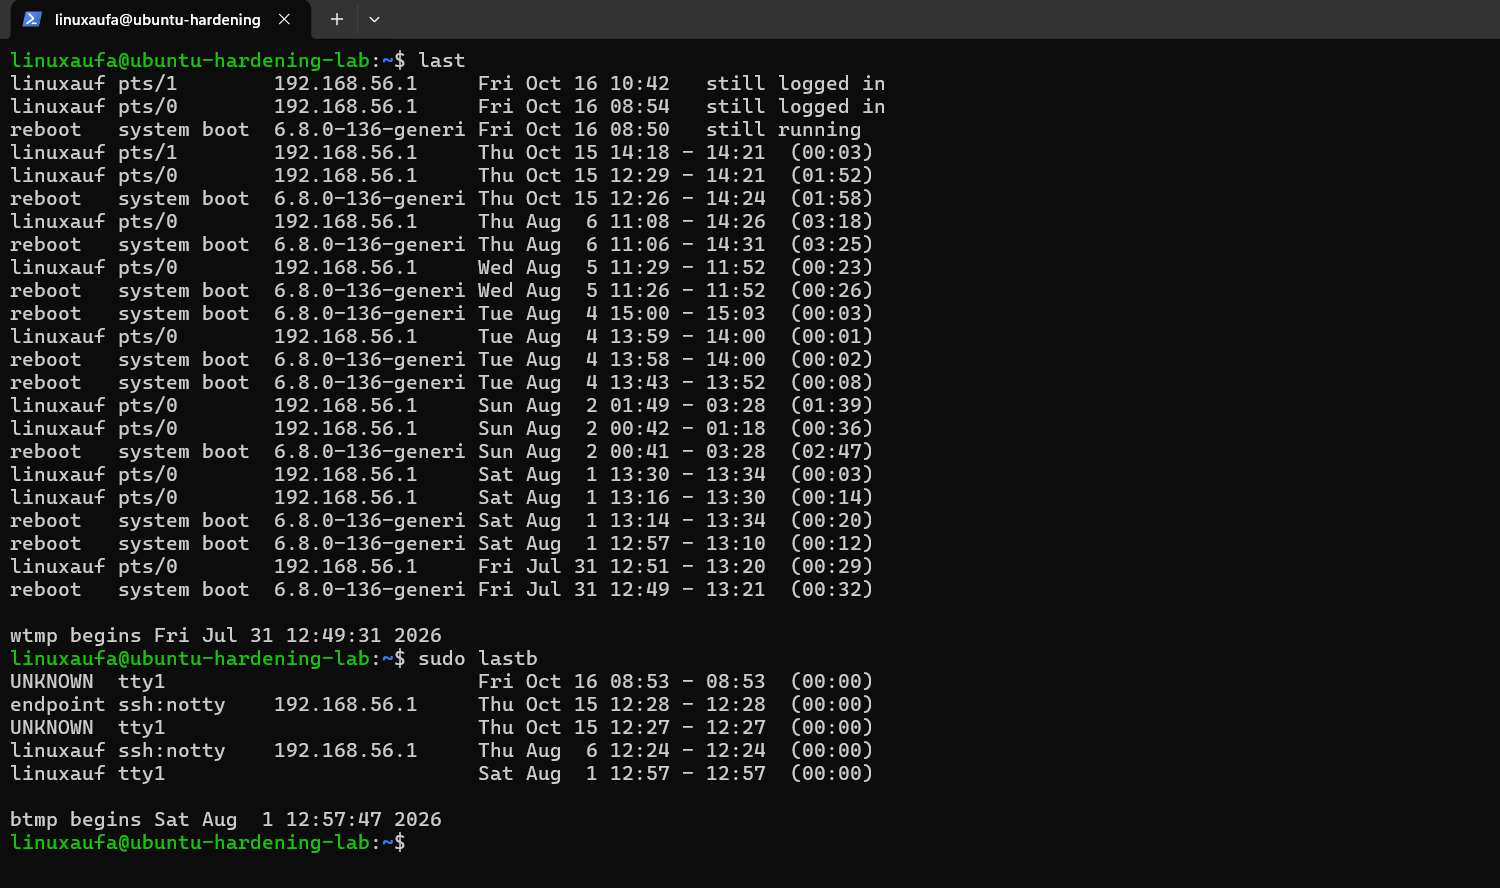
Historical Session Analysis (last and lastb)
Historical session auditing: correlated successful and failed authentication sessions via last and lastb binary log inspection.
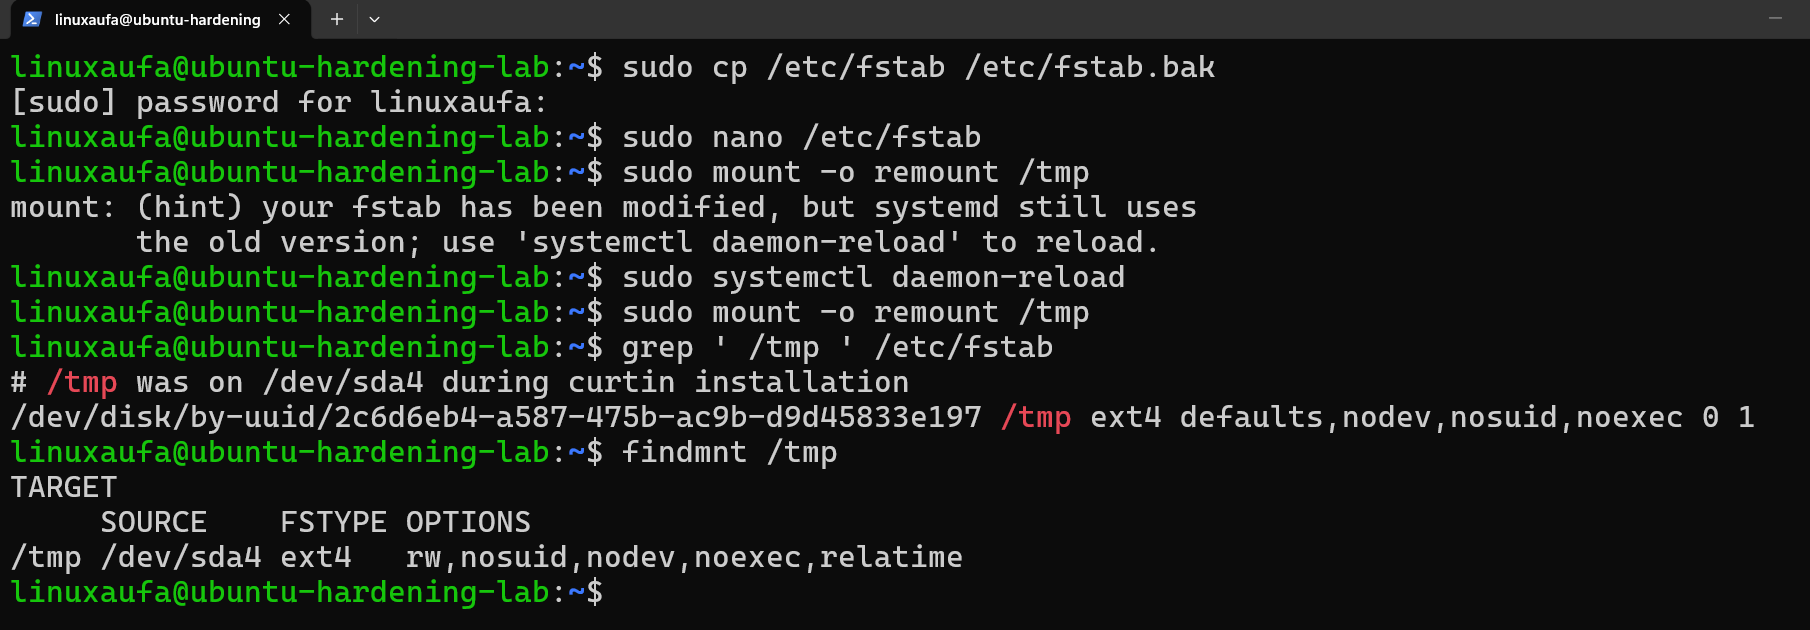
Hardened /tmp Mount Options in fstab
Hardened /tmp filesystem mount options: enforced nosuid, nodev, and noexec flags in /etc/fstab and verified active in findmnt.
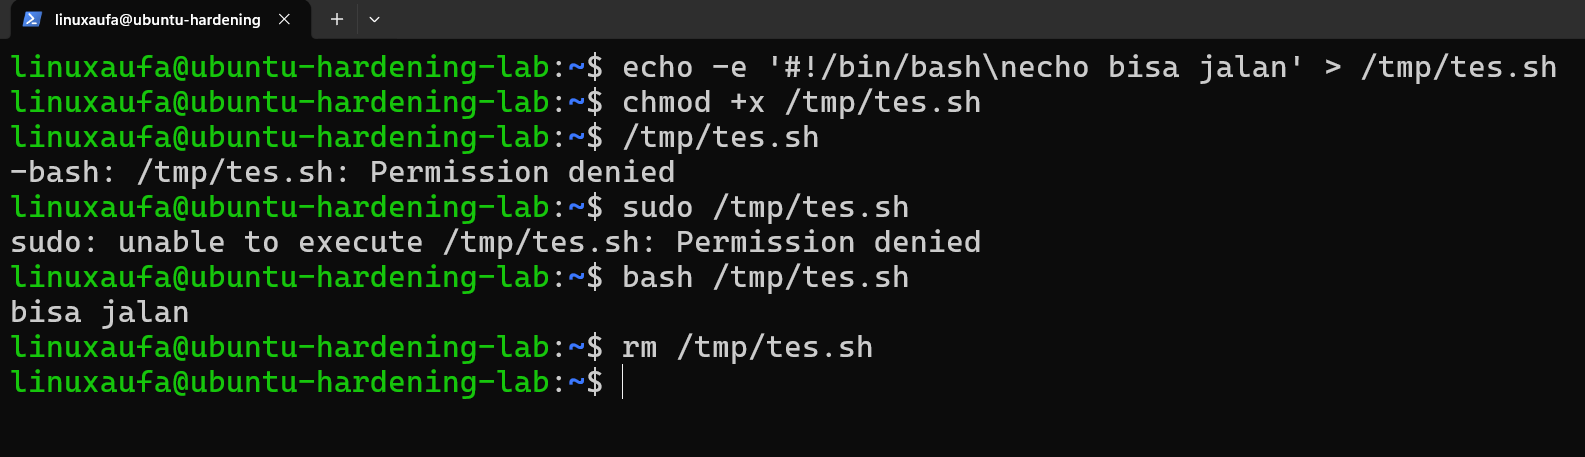
Execution Prevention Test on /tmp
Runtime execution restriction validation: direct binary execution on /tmp successfully blocked with 'Permission denied'.
Investigation Timeline
Custom Partitioning & FHS Baseline Configuration
Provisioned Ubuntu Server 24.04 LTS with 6 isolated partitions (/ 15G, swap 4G, /tmp 3G, /var 5G, /var/log 5G, /home 5G). Generated fresh-install-before-hardening VM snapshot as baseline anchor.
Authentication Forensics & Log Pattern Evaluation
Simulated failed SSH login attempts from host. Discovered that generic grep queries miss Invalid user entries and introduce noise from sudo session PAM events, informing robust parsing logic for future audit scripts.
Filesystem Hardening: Restricting /tmp Mount Options
Configured nodev, nosuid, and noexec options on /tmp in /etc/fstab. Executed systemctl daemon-reload and mount -o remount /tmp, confirming active enforcement via findmnt and verifying binary execution denial.
GRUB Initramfs Timing Triage & Recovery
Investigated persistent boot hangs at loading essential drivers on virtualized storage. Formulated and tested timing hypotheses, successfully establishing repeatable GRUB edit mode workarounds.
Implementation Phases & Checklist
- ✓Install Ubuntu Server 24.04.4 LTS on VirtualBox (standard non-minimized)
- ✓Configure dual network adapters (NAT + Host-only) and verify remote SSH access
- ✓Create clean VM baseline snapshot: fresh-install-before-hardening
- ✓Execute custom 6-partition scheme (/ 15G, swap 4G, /tmp 3G, /var 5G, /var/log 5G, /home 5G)
- ✓Initialize git repository directory structure and initial commit
- ✓Audit FHS top-level directory roles (/etc, /var, /tmp, /proc, /sys, /boot, /home)
- ✓Evaluate security boundaries of /etc/passwd (644) vs /etc/shadow (640)
- ✓Analyze auth.log, last, and lastb telemetry during simulated SSH failures
↳ Identified grep blind spots on Invalid user and sudo noise
- ✓Document blue team staging risks: why /tmp and /dev/shm attract adversary payloads
- ○Review merged-usr symlinks (/bin, /sbin, /lib -> /usr) and man hier specifications
- ✓Enforce separate partitions for /tmp, /var, /var/log, and /home
- ✓Configure nodev, nosuid, noexec on /tmp in /etc/fstab and verify via findmnt
↳ Execution test confirmed: direct execution denied
- ◐Mount /dev/shm with nodev, nosuid, noexec flags
↳ Remount procedure prepared, awaiting execution test confirmation
- ○Enforce nodev and nosuid on /var and /home, and nodev/nosuid/noexec on /var/log
- ○Install and initialize AIDE filesystem integrity checking database
- ○Blacklist legacy unused filesystems (cramfs, freevxfs, jffs2, hfs, hfsplus, udf)
- ○Blacklist usb-storage kernel module to prevent unauthorized removable media
- ○Restrict /boot/grub/grub.cfg permissions to root-only read/write (0600)
- ○Verify ASLR enforcement (kernel.randomize_va_space = 2)
- ○Restrict core dumps (fs.suid_dumpable = 0) and limits.conf hard limits
- ○Enforce AppArmor enabled in enforce mode across standard profiles
- ○Disable unneeded legacy services (avahi-daemon, cups, rpcbind, samba)
- ○Audit and baseline listening ports (ss -tulpn) to ensure minimal attack surface
- ○Configure kernel network sysctl parameters: disable IP forwarding and ICMP redirects
- ○Enable TCP SYN cookies (net.ipv4.tcp_syncookies = 1) and rp_filter anti-spoofing
- ○Configure UFW firewall: default deny incoming, permit SSH from Host-only subnet exclusively
- ○Disable unused network protocols (dccp, sctp, rds, tipc)
- ✓Verify baseline permissions: /etc/passwd (644) and /etc/shadow (640)
- ✓Audit sudo group membership (verified restricted to primary user linuxaufa)
- ○Harden SSH daemon: PermitRootLogin no, PasswordAuthentication no, MaxAuthTries 4
- ○Enforce PAM password complexity via pam_pwquality and pam_pwhistory
- ○Configure account lockout policy after consecutive failed logins via pam_faillock
- ○Install and configure auditd rules for sensitive file changes and identity files
- ○Set default umask to 027 and enforce shell idle timeout (TMOUT=900)
- ○Develop check_tmp_mount_options (nodev, nosuid, noexec on /tmp)
- ○Develop check_dev_shm_mount_options (noexec on /dev/shm)
- ○Develop check_passwd_permissions and check_shadow_permissions
- ○Develop check_ssh_root_login and check_ssh_password_auth
- ○Develop check_unnecessary_services and check_firewall_status
- ○Develop check_sysctl_network parameters and check_ip_forwarding
- ○Develop check_auditd_status and check_aide_installed
- ○Develop check_ssh_bruteforce_log tracking failed attempts per IP from auth.log
- ○Assemble 21 modular check functions into unified linux-hardening-audit.sh tool
- ○Document before-and-after compliance metrics and audit execution reports
- ○Compile full investigation writeup (writeup.md) and troubleshooting notes
- ◐Document initramfs boot hang troubleshooting and GRUB timing workaround
↳ GRUB recovery verified, hardware timing hypothesis under evaluation
- ○Publish complete linux-hardening-audit repository to GitHub
Documentation & Technical Reports
Comprehensive technical analysis, investigation methodology, and formal security documentation for this project are currently being compiled. The full report and lab artifacts will be published here soon.
This project was developed strictly for cybersecurity education, system defense research, and professional portfolio demonstration. All hardening configurations and simulated authentication failures were performed within an isolated, self-hosted virtual machine (VirtualBox Host-only network) targeting owned lab assets exclusively.